TechLogHub Blog — Page 17 of 25
Insights, guides, and product strategy for builders and product teams.

Inside Caller-as-a-Service Fraud: The Scam Economy Has a Hiring Process
This post exposes Caller-as-a-Service, a structured, scalable fraud operation that treats phone scams like a professional business. It maps a full attack lifecycle with distinct roles—from data sourcing and infrastructure to live-call agents—supervision, and varied compensation models. It explains underground recrui…

Microsoft Releases Emergency Patches for Critical ASP.NET Core Privilege Escalation Flaw
Microsoft issued out-of-band security updates to patch a critical ASP.NET Core Data Protection vulnerability (CVE-2026-40372) that could allow attackers to forge authentication cookies and escalate to SYSTEM privileges. The flaw stems from a regression in DataProtection packages 10.0.0–10.0.6, where the HMAC validat…

Over 1,300 Microsoft SharePoint servers vulnerable to spoofing attacks
More than 1,300 Microsoft SharePoint servers remain online and unpatched against CVE-2026-32201, a spoofing vulnerability affecting SharePoint Server 2016, 2019, and Subscription Edition. Exploitation could allow attackers to view or modify sensitive data with a low-complexity, no-interaction attack, though it canno…

French govt agency confirms breach as hacker offers to sell data
France’s ANTS agency confirms a data breach after a threat actor claimed access to the ants.gouv.fr portal, potentially exposing up to 19 million records. Exposed data include login IDs, full names, emails, dates of birth, unique account IDs, and some postal addresses, places of birth, and phone numbers, with the br…

KelpDAO Hit by $290 Million Heist Linked to Lazarus Hackers
North Korea’s Lazarus Group is suspected to have stolen about $290 million from KelpDAO by exploiting a compromised cross-chain verification layer to drain roughly 116,500 rsETH (around $293 million) and move funds through Tornado Cash. The attack also affected Compound and Euler, with Aave freezing rsETH deposits/b…

China's Apple App Store infiltrated by crypto-stealing wallet apps
Security researchers have uncovered 26 fake crypto-wallet apps on Apple's App Store in China that impersonate wallets like MetaMask, Coinbase, Trust Wallet, and OneKey to steal seed phrases. The FakeWallet campaign, linked to SparkKitty, used typosquatting and spoofed branding and was disguised as games or calculato…

The Gentlemen ransomware now uses SystemBC for bot-powered attacks
Check Point reveals that The Gentlemen ransomware affiliate network has begun using SystemBC proxy malware, forming a botnet of over 1,570 hosts to covertly deliver payloads and support post‑exploitation operations, signaling a shift toward a broader, more mature toolchain targeting corporate environments across the…

NIST to stop rating non-priority flaws due to volume increase
NIST’s National Vulnerability Database will stop assigning severity scores to lower-priority vulnerabilities due to a surge in submissions. Beginning April 15, 2026, CVEs will be enriched only if they meet risk-based criteria: they appear in CISA’s Known Exploited Vulnerabilities catalog, affect U.S. federal softwar…

Vercel confirms breach as hackers claim to be selling stolen data
Vercel confirms a security incident after a third-party AI tool’s Google Workspace OAuth app was compromised, with attackers claiming to sell stolen data. The breach allegedly allowed access to non‑sensitive environment variables and, later, broader access; Vercel says core services remain unaffected and is working …

Microsoft releases emergency updates to fix Windows Server issues
Microsoft issued emergency out-of-band updates to fix issues caused by April 2026 security updates for Windows Server, including installation failures on Windows Server 2025, LSASS-related domain controller restart loops, and BitLocker recovery prompts after KB5082063, with fixes covering Windows Server 2025, 23H2, …

Microsoft tests Windows Explorer speed, performance improvements
Microsoft is testing Windows 11 File Explorer speed and performance improvements for Insider users, including an optional background preloading feature to speed launches. The rollout also includes reliability fixes (stopping explorer.exe) and dark-mode white-flash fixes, building on the May 2025 Startup Boost for Of…

Microsoft Pulls Service Update Causing Teams Launch Failures
Microsoft has reverted a service update that caused Teams desktop launch failures due to a regression in the client build caching system; users experiencing the issue should fully quit and restart Teams for the fix to propagate, while Microsoft continues to monitor telemetry and seek confirmation that the incident i…

Seiko USA website defaced as hacker claims customer data theft
Seiko USA’s website was defaced with a ransom note claiming the Shopify-backed customer database was breached and exfiltrated, threatening to publish sensitive data unless a 72-hour negotiation window is met. The attackers allege they obtained names, emails, phone numbers, order histories, shipping details, and acco…

Recently leaked Windows zero-days now exploited in attacks
Threat actors are actively exploiting three newly disclosed Windows zero-days—BlueHammer, RedSun, and UnDefend—to gain SYSTEM or elevated privileges and to block Defender updates. BlueHammer has been patched in the April 2026 updates (CVE-2026-33825), but RedSun and UnDefend remain unpatched, enabling attacks on Win…

CISA flags Apache ActiveMQ flaw as actively exploited in attacks
CISA warns that the high-severity CVE-2026-34197 flaw in Apache ActiveMQ is now actively exploited in attacks. The vulnerability enables remote code execution through improper input validation and was patched on March 30 for ActiveMQ Classic 6.2.3 and 5.19.4; ShadowServer reports over 7,500 exposed servers. CISA add…

Webinar: From phishing to fallout — Why MSPs must rethink both security and recovery
BleepingComputer is hosting a live webinar on May 14, 2026 at 2:00 PM ET with Kaseya to explain why MSPs must rethink both security and recovery, highlighting how AI-powered phishing, BEC, and ransomware challenge traditional defenses and how integrating SaaS backups and disaster recovery with prevention and detecti…

Inside an Underground Guide: How Threat Actors Vet Stolen Credit Card Shops
Flare’s analysis reveals an underground guide that treats vetting stolen credit card shops as the core skill, showing threat actors moving from opportunistic fraud to structured supplier verification. Survival and data freshness define legitimacy, with emphasis on fresh BIN data and low decline rates, multiple data …
Grinex Exchange Blames Western Intelligence for $13.7M Crypto Hack
Grinex, a Kyrgyzstan-based exchange with Russian ties, suspended operations after a $13.7 million hack targeting Russian user wallets. The exchange claims Western intelligence orchestrated the attack to undermine Russia’s financial sovereignty, but no public evidence supports this attribution. Security researchers t…
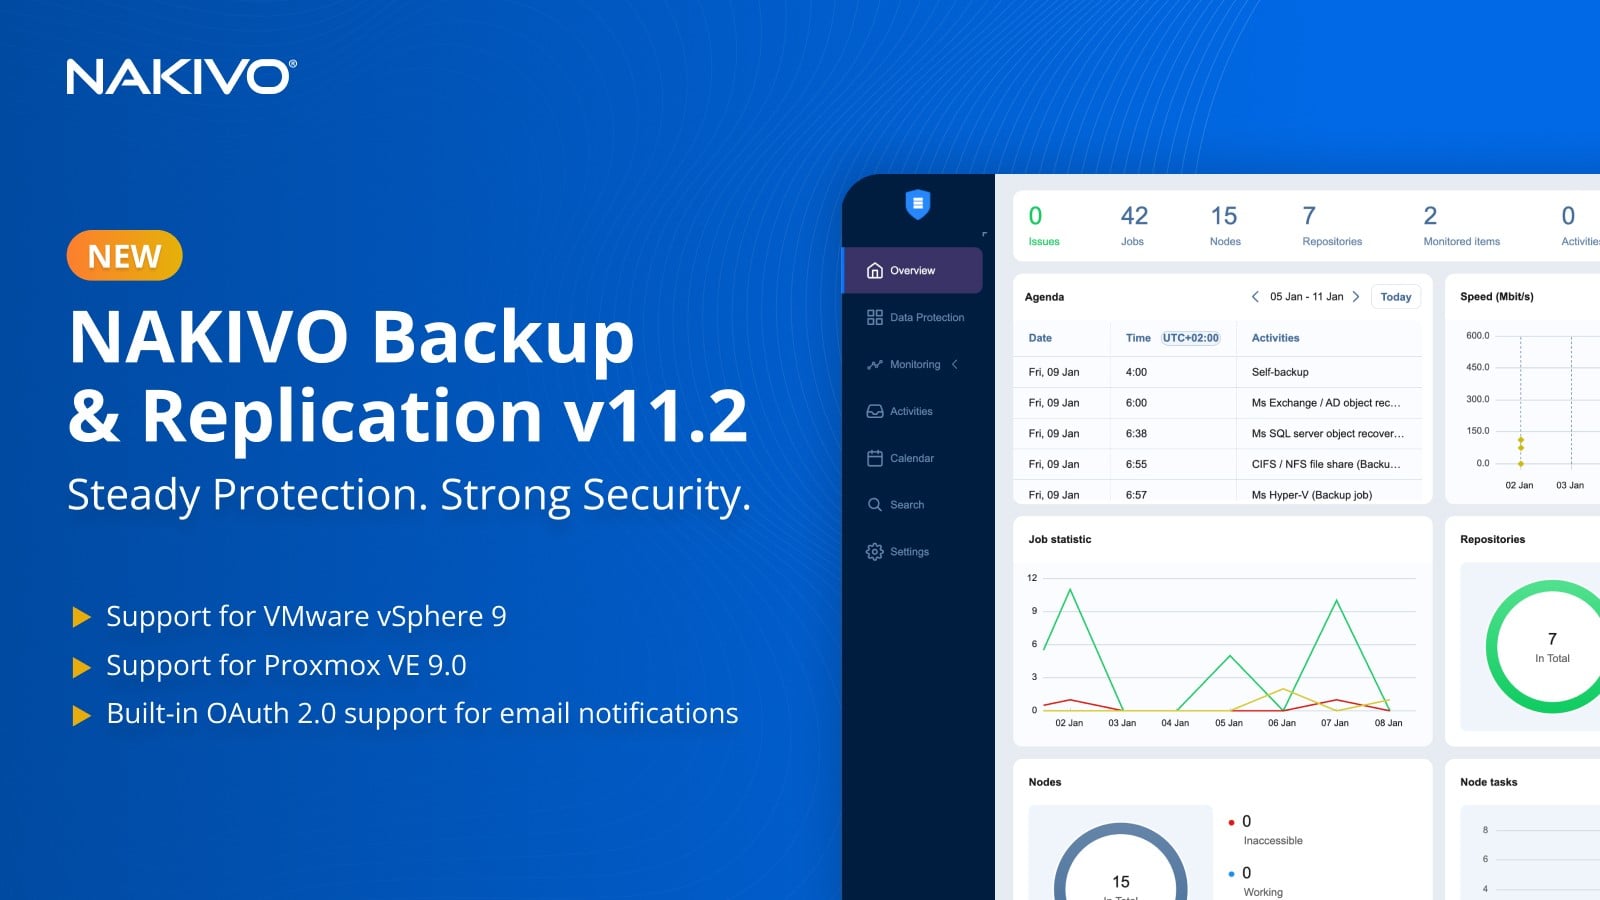
NAKIVO v11.2: Ransomware Defense, Faster Replication, vSphere 9, and Proxmox VE 9.0 Support
NAKIVO announces the general availability of Backup & Replication v11.2, featuring automated real-time replication, full VMware vSphere 9 support, Proxmox VE 9.0/9.1 compatibility, OAuth 2.0 for secure notifications, and expanded ransomware defenses with immutable backups and air-gapped options, plus an enhanced MSP…

Microsoft Teams right-click paste broken by Edge update bug
Microsoft warns that a recent Edge browser update breaks the right-click paste function in Microsoft Teams desktop chats; users should use keyboard shortcuts (Ctrl/C/V on Windows, Cmd/C/V on macOS) while Microsoft rolls out a staged fix with no exact ETA as of April 16, 2026.
Showing 20 of 485 articles