Insights, Guides & Product Strategy
Learn how teams discover, evaluate, and ship faster with the right tools.
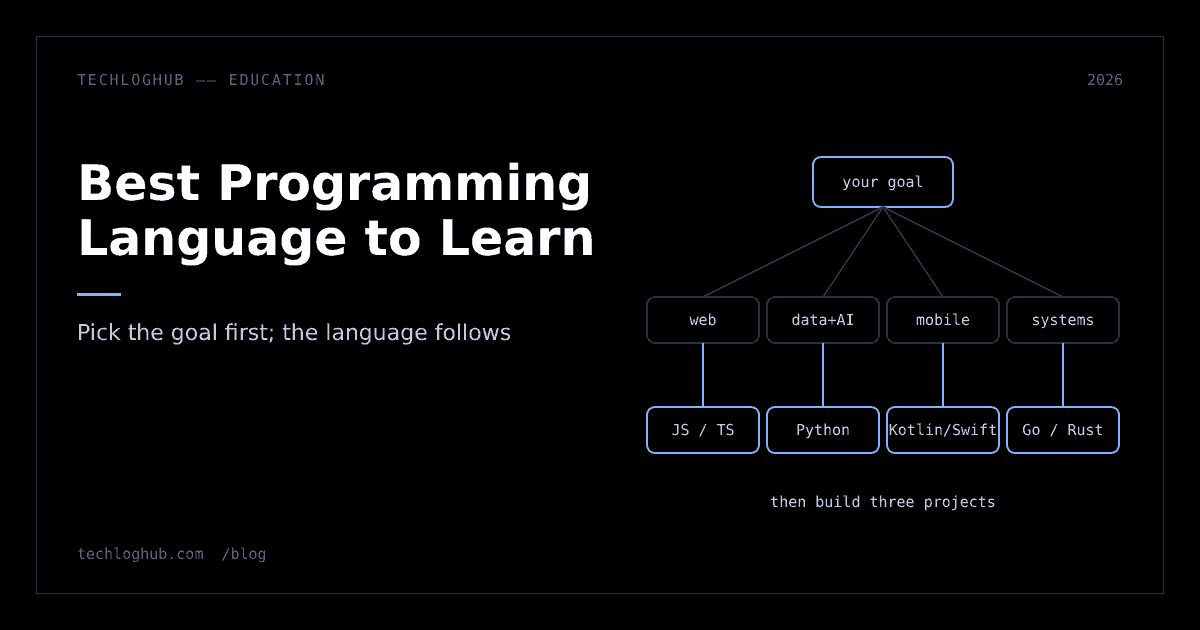
Best Programming Language to Learn in 2026: A Decision Guide by Goal
Which language to learn first in 2026, by goal: web, data and AI, mobile, systems, games or jobs, checked against Stack Overflow, GitHub and TIOBE data.
20 Python Projects for Beginners, Graded by Difficulty (With Code)
20 Python projects for beginners in three difficulty levels, each with a goal, the skills it teaches, runnable starter code and stretch goals to keep going.
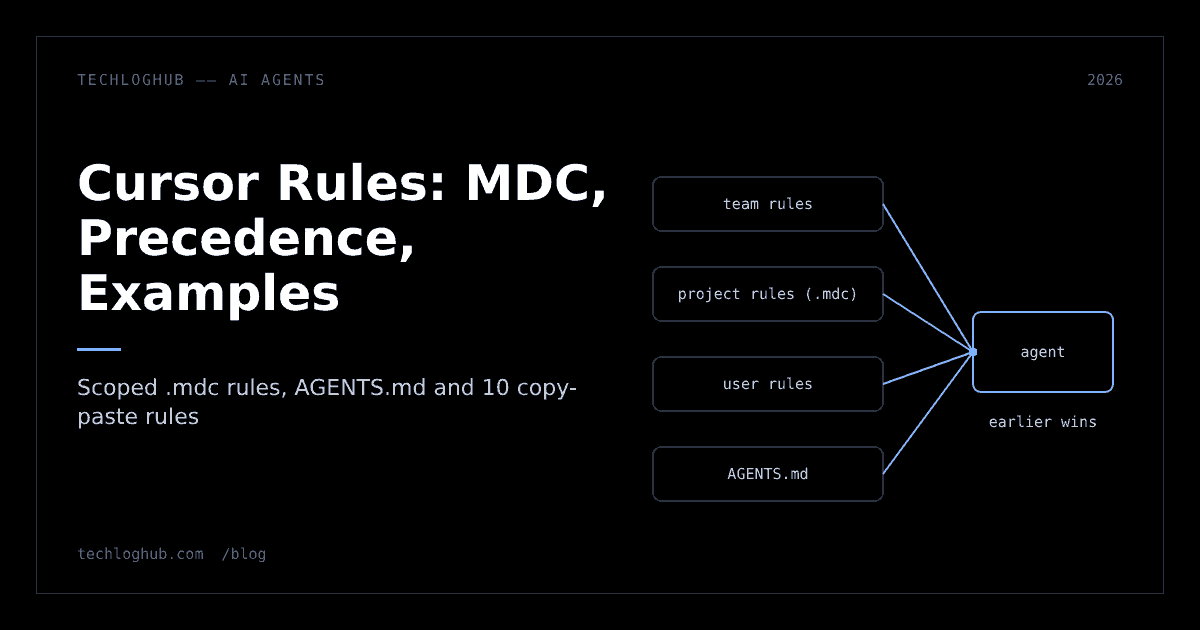
Cursor Rules: .cursor/rules, MDC Format and 10 Copy-Paste Examples
How Cursor rules work in 2026: .cursor/rules MDC files, the four apply modes, precedence, AGENTS.md, legacy .cursorrules, and 10 copy-paste rule examples.
SaaS Ideas: 25 Micro SaaS Ideas With Real Demand, and How to Test Them
25 micro SaaS ideas tied to demand you can check: new rules, deadlines, platform shifts and developer pain. Plus how to find, validate and price your own.
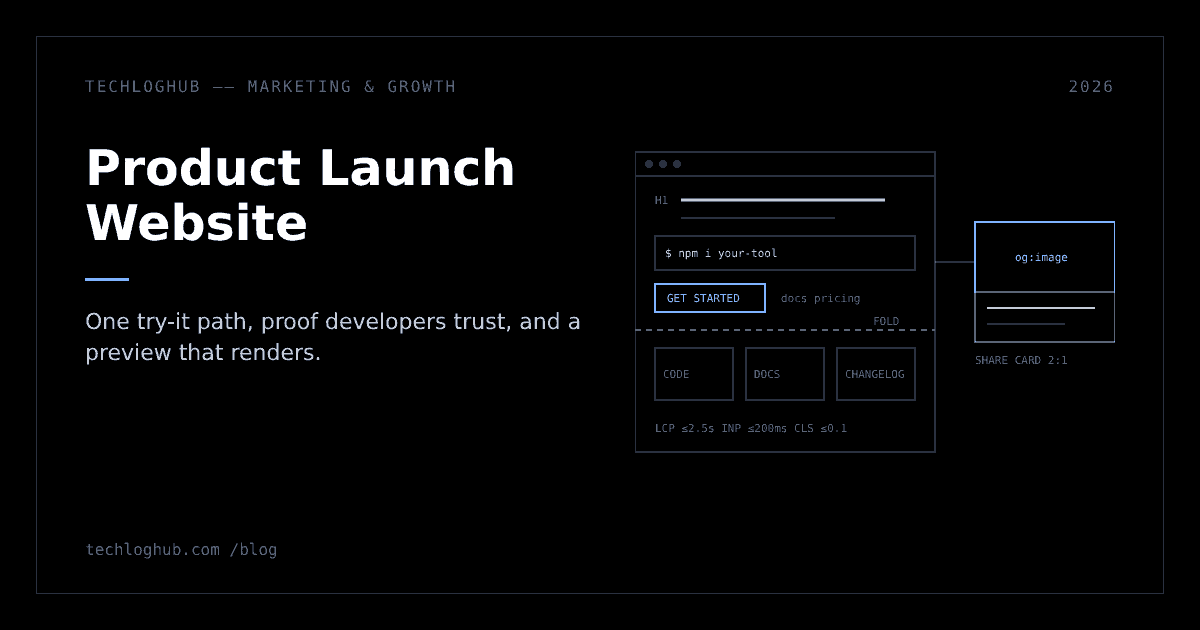
Product Launch Website: What a Dev Tool Launch Page Needs
What a product launch website for a dev tool needs: one try-it call to action, above-the-fold answers, proof, share previews, speed targets and SEO basics.
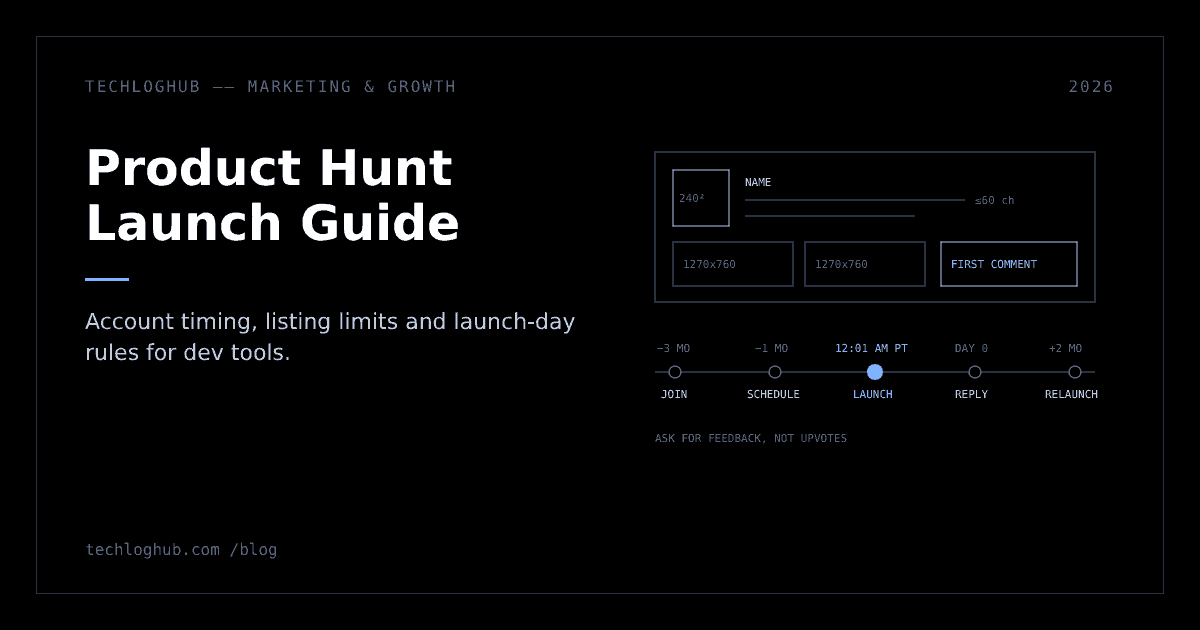
Product Hunt Launch Guide for Developer Tools (2026 Rules)
A current Product Hunt launch guide for dev tools: account timing, self-hunting, listing limits, first comment, 12:01 AM PT scheduling and launch-day rules.
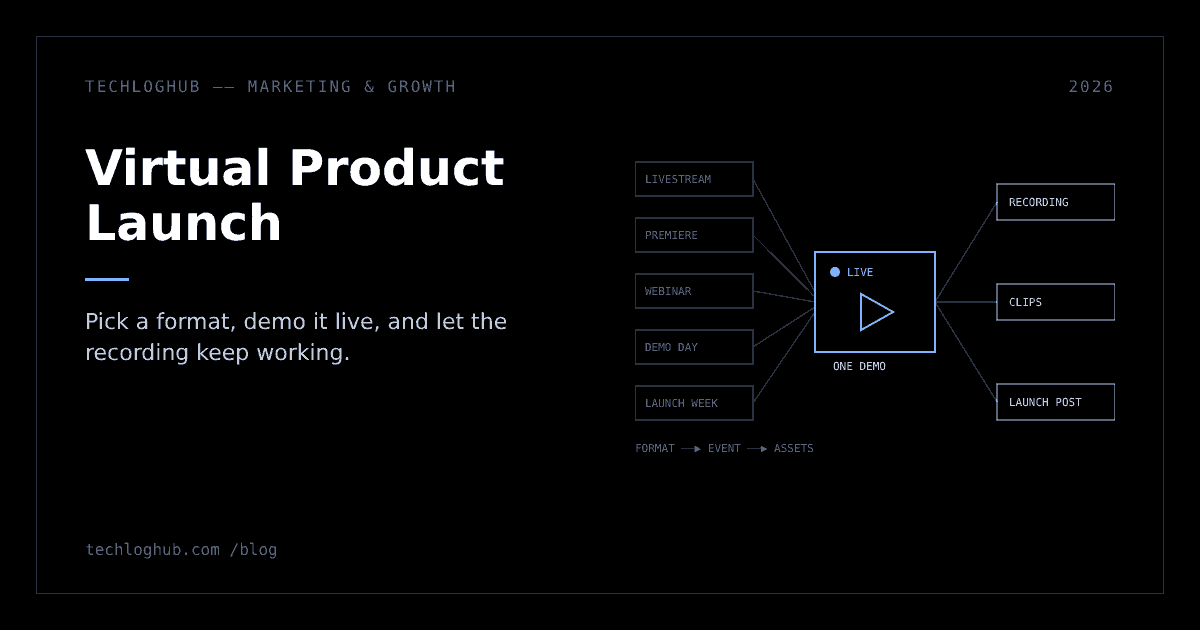
Virtual Product Launch: How to Run an Online Launch for a Dev Tool
How to run a virtual product launch for a dev tool: livestream, premiere, webinar or launch week, plus production setup, run of show and post-event reuse.
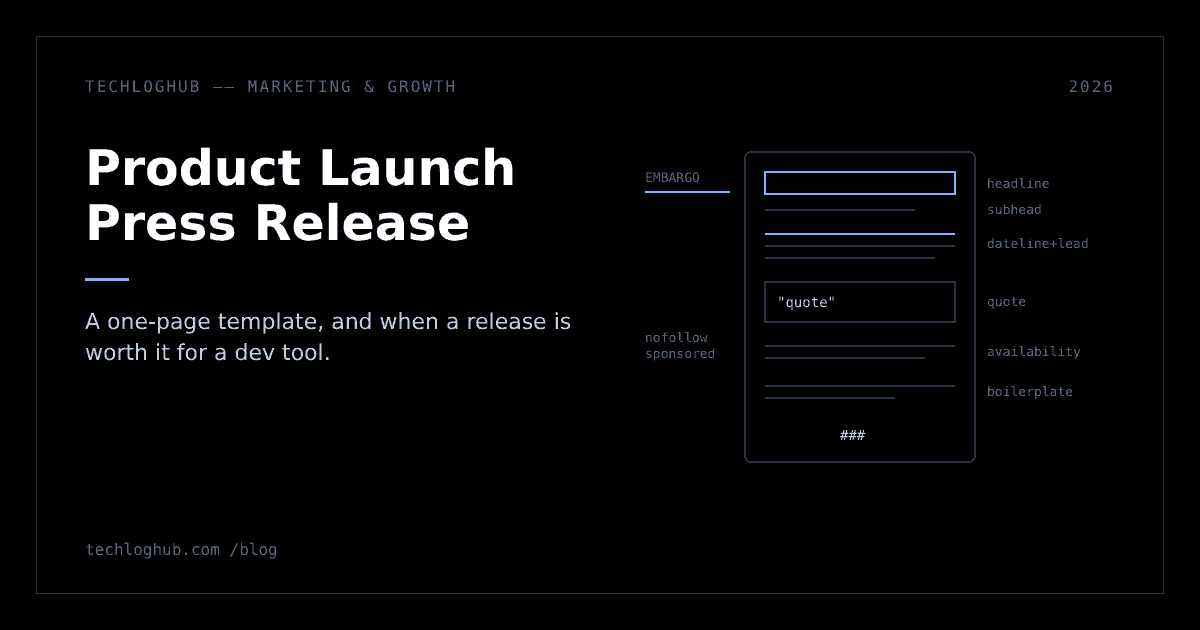
Product Launch Press Release: Template and When It's Worth It
A product launch press release template for dev tools and SaaS: when a release is worth it, how to pitch it, and the SEO link rules to follow when distributing.
SaaS Product Launch: From MVP and Soft Launch to Feature Launches
A SaaS product launch guide: launching an MVP, running a soft launch, feature flags to separate deploy from release, sizing feature launches, B2B launches.
Pre-Launch Marketing Strategy for Developer Tools and SaaS
Pre-launch marketing strategy for dev tools: build a pre-launch website that converts, run a compliant waitlist, publish useful content, prep launch channels.
Product Launch Checklist for Dev Tools: Every Step, Phase by Phase
A product launch checklist for developer tools and SaaS, grouped by phase from week −8 to week 4, with an owner and a done-when test for every launch step.
Product Launch Strategy for Dev Tools and SaaS: A Practical Playbook
A step-by-step product launch strategy for dev tools and SaaS: positioning, a pre-launch list, Show HN and Product Hunt rules, a launch-day timeline, metrics.
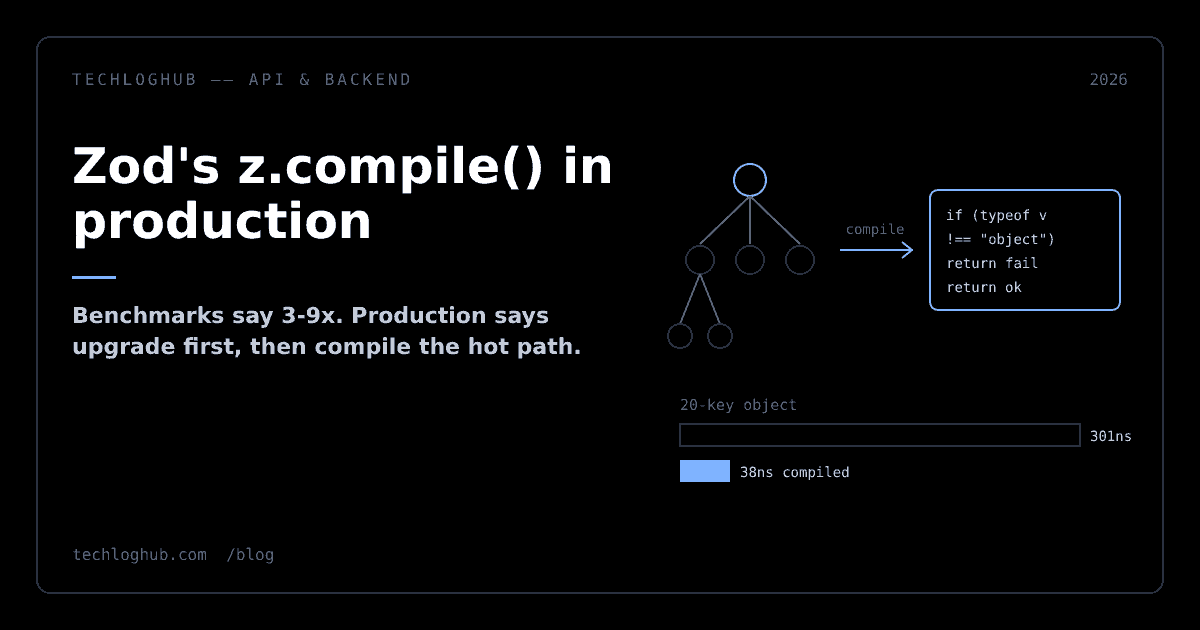
Zod's z.compile(): Where the Speedup Shows Up in Production
Zod 4.5's z.compile() parses 3-9x faster in benchmarks, but Trigger.dev's production data tells a smaller story. When to turn it on and what to check first.
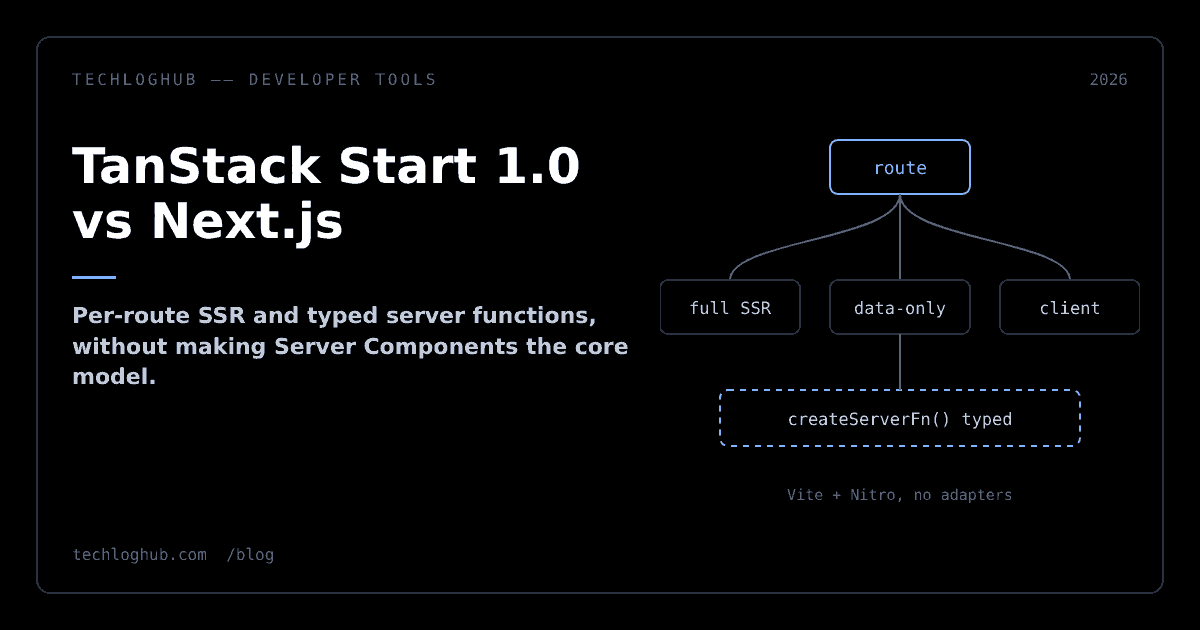
TanStack Start 1.0 Is Stable: When It Beats Next.js, When It Doesn't
TanStack Start 1.0 shipped as a stable full-stack React framework. What 1.0 commits to, how it differs from Next.js, and who should actually migrate.
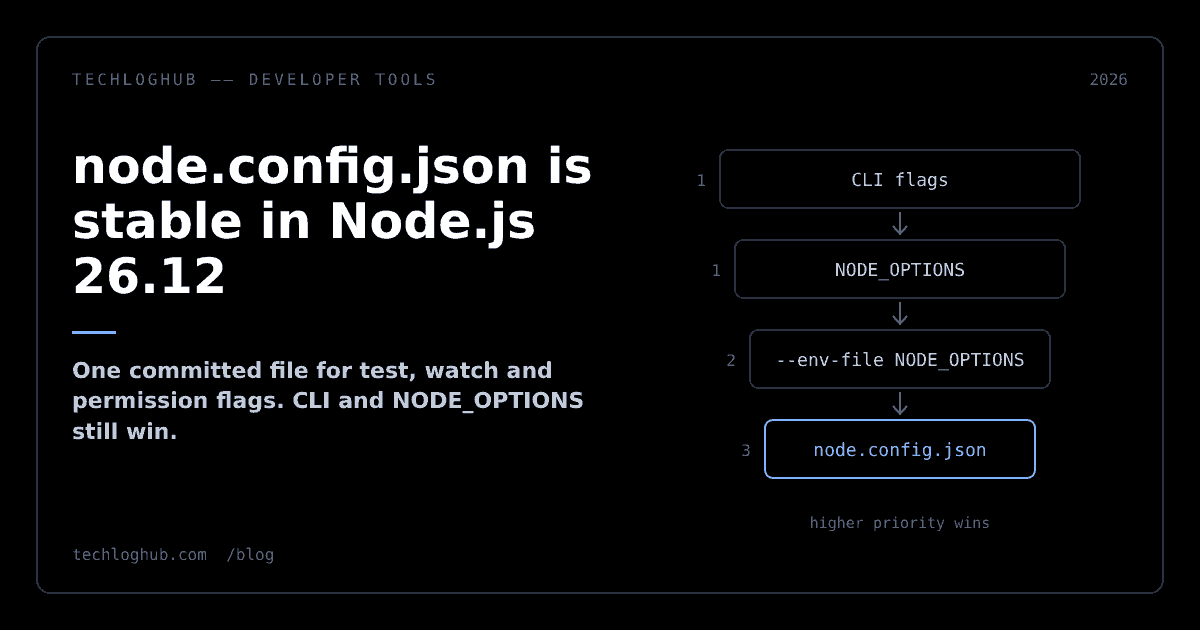
Node.js 26.12 Makes node.config.json Stable: What to Move Into It
Node.js 26.12 marks the config file stable and renames the flag to --config-file. What belongs in node.config.json, the precedence rules, and the traps.
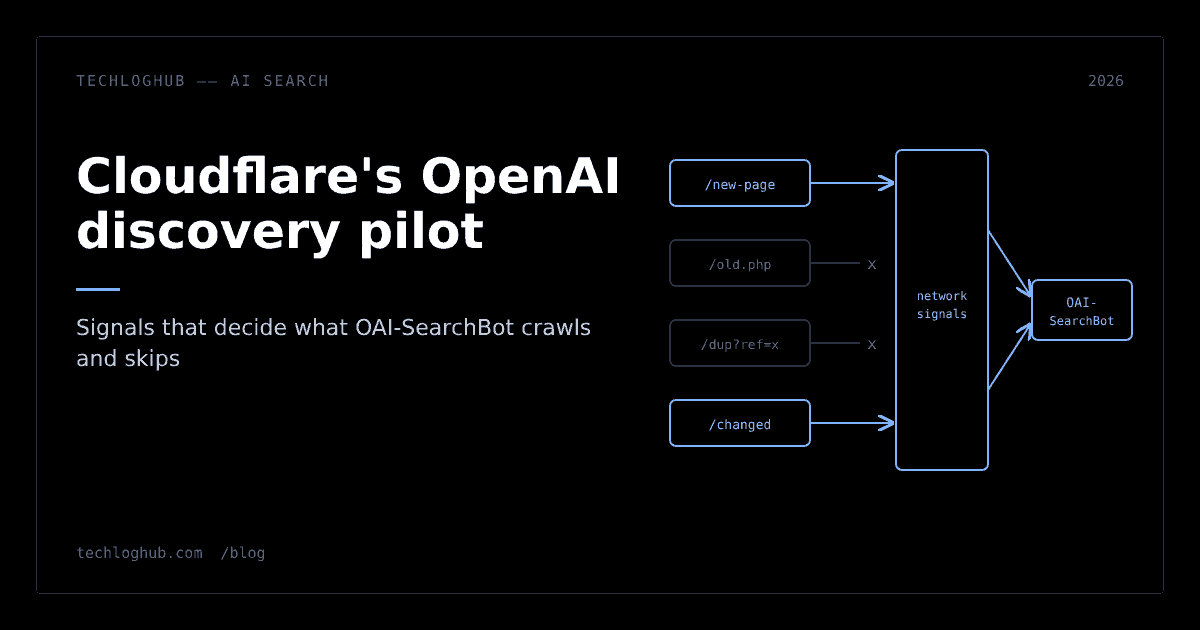
Cloudflare's OpenAI Discovery Pilot: What Site Owners Should Change
Cloudflare now feeds network signals to OpenAI's search crawler. How the pilot works, what it skips, and the robots.txt and URL fixes worth making now.
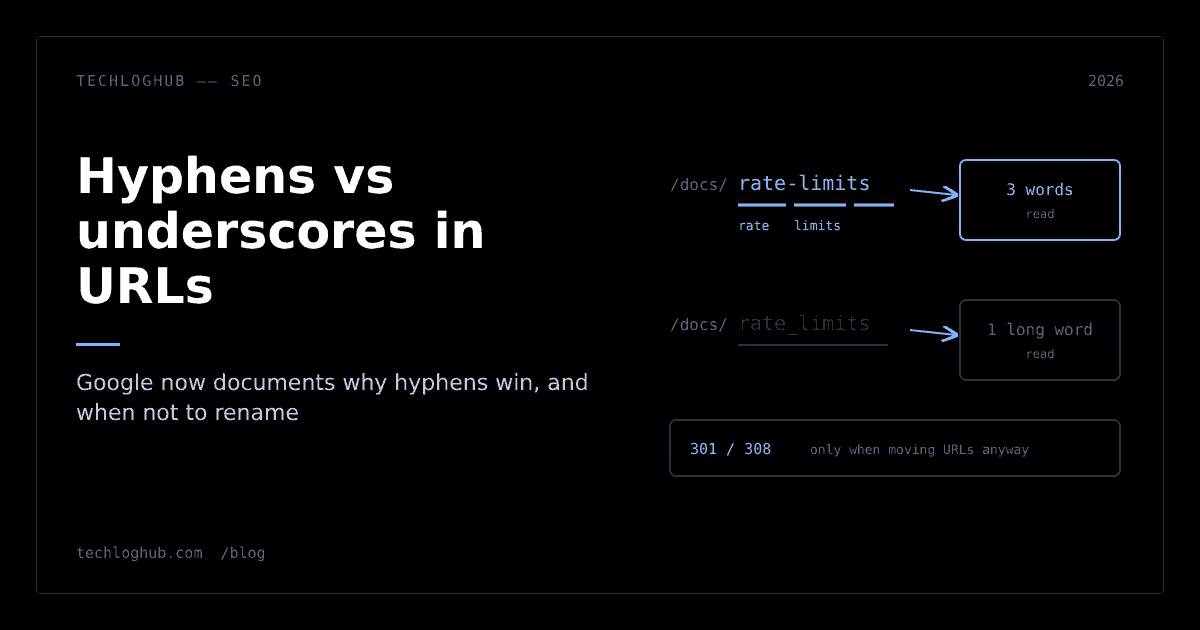
Hyphens vs Underscores in URLs: What Google's Updated Doc Says
Google's URL structure doc now explains why hyphens beat underscores. What changed, what Gary Illyes said, and when renaming existing URLs is worth it.
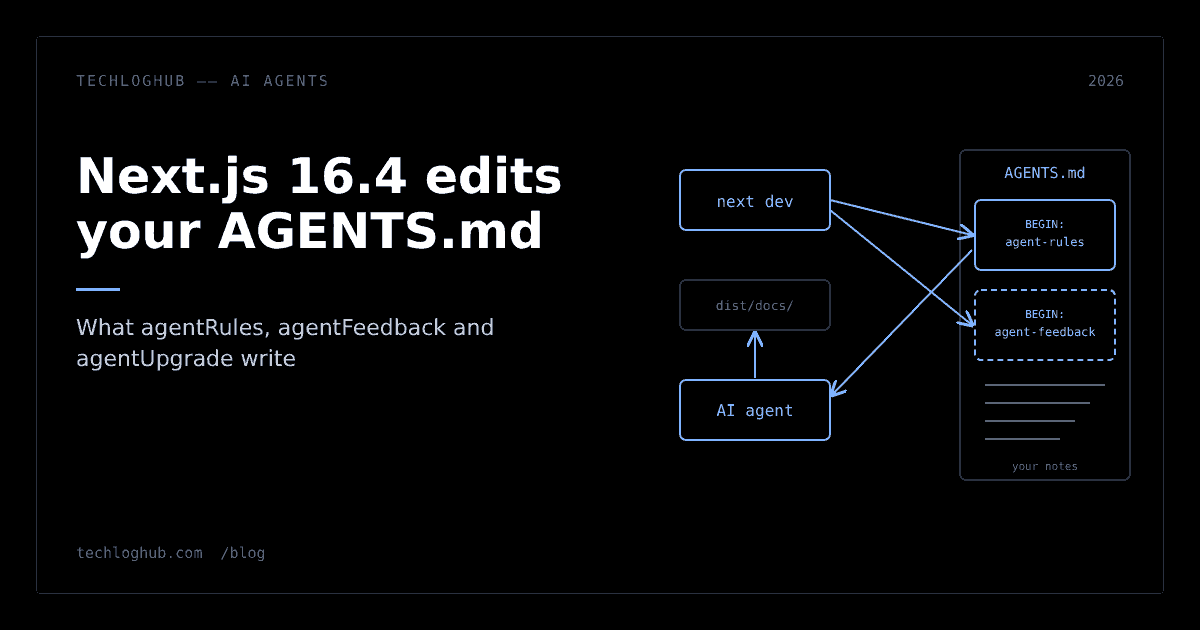
Next.js 16.4 Edits Your AGENTS.md: What to Keep and What to Turn Off
Next.js 16.4 writes and restores managed blocks in AGENTS.md. What agentRules, agentFeedback and agentUpgrade do, their defaults, and which to turn off.
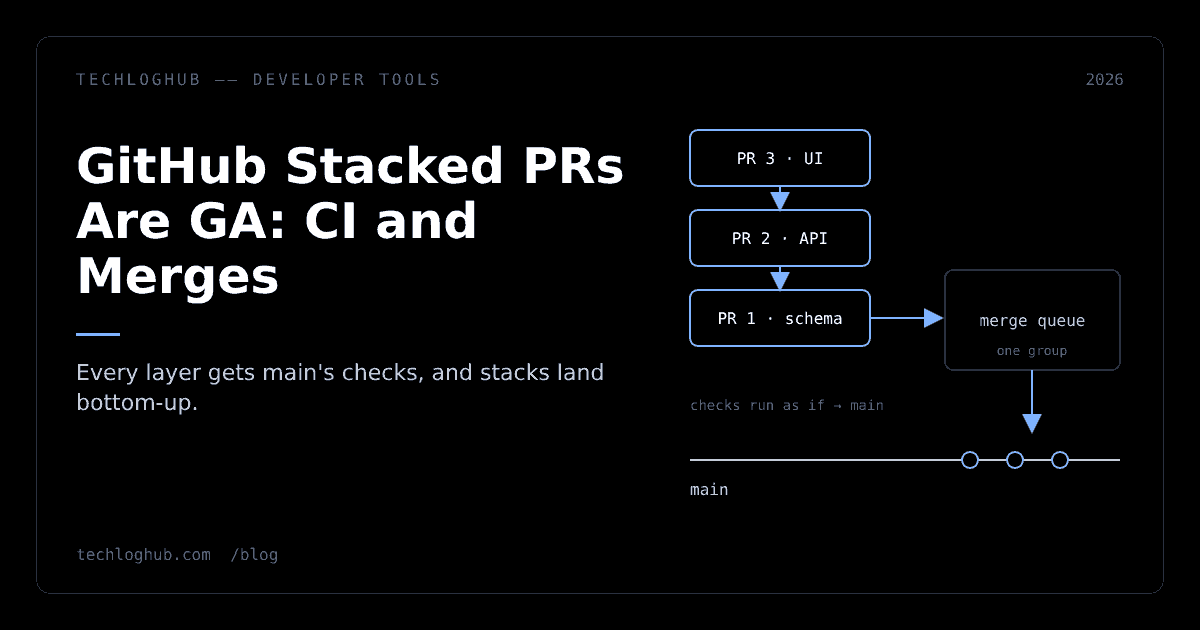
GitHub Stacked Pull Requests Are GA: What Changes for CI and Merges
GitHub stacked pull requests are GA on all plans. How branch protections, required checks and the merge queue treat each layer, plus gh stack and the limits.
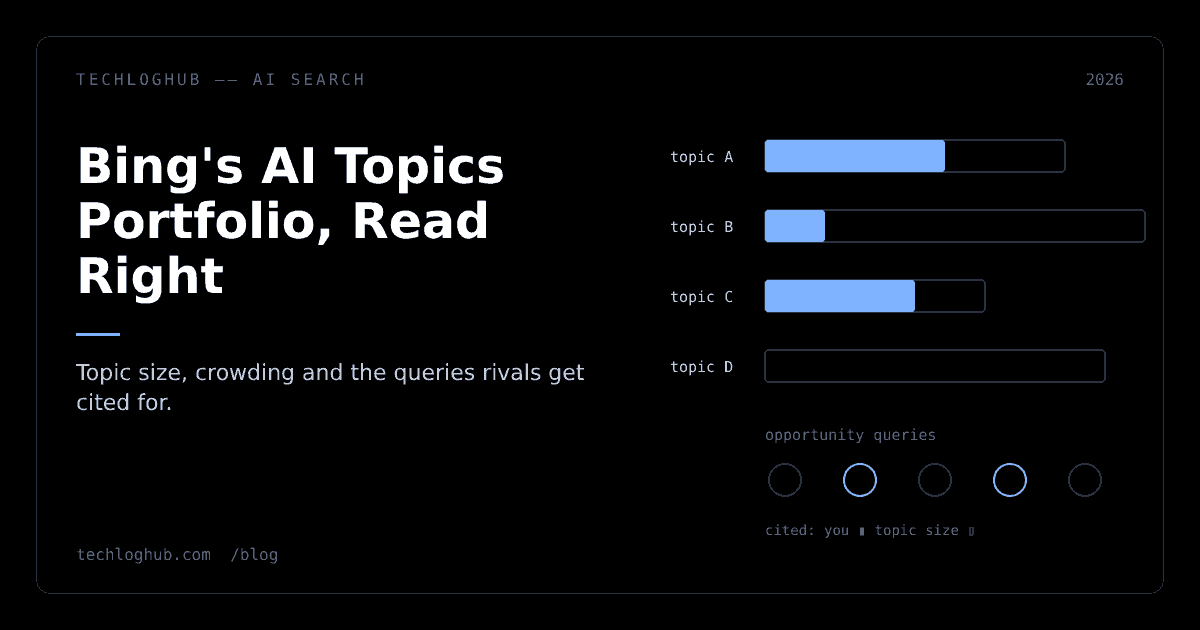
Bing's AI Topics Portfolio: How to Read Opportunity Queries
Bing Webmaster Tools now clusters your AI grounding queries into topics and lists where rivals get cited and you don't. What the numbers mean and how to act.
Showing 20 of 485 articles
All articles
Every published post, newest first — 485 in total.
November 2026
- Best Programming Language to Learn in 2026: A Decision Guide by Goal
- 20 Python Projects for Beginners, Graded by Difficulty (With Code)
- Cursor Rules: .cursor/rules, MDC Format and 10 Copy-Paste Examples
- SaaS Ideas: 25 Micro SaaS Ideas With Real Demand, and How to Test Them
- Product Launch Website: What a Dev Tool Launch Page Needs
- Product Hunt Launch Guide for Developer Tools (2026 Rules)
- Virtual Product Launch: How to Run an Online Launch for a Dev Tool
- Product Launch Press Release: Template and When It's Worth It
- SaaS Product Launch: From MVP and Soft Launch to Feature Launches
- Pre-Launch Marketing Strategy for Developer Tools and SaaS
- Product Launch Checklist for Dev Tools: Every Step, Phase by Phase
- Product Launch Strategy for Dev Tools and SaaS: A Practical Playbook
October 2026
- Zod's z.compile(): Where the Speedup Shows Up in Production
- TanStack Start 1.0 Is Stable: When It Beats Next.js, When It Doesn't
- Node.js 26.12 Makes node.config.json Stable: What to Move Into It
- Cloudflare's OpenAI Discovery Pilot: What Site Owners Should Change
- Hyphens vs Underscores in URLs: What Google's Updated Doc Says
- Next.js 16.4 Edits Your AGENTS.md: What to Keep and What to Turn Off
- GitHub Stacked Pull Requests Are GA: What Changes for CI and Merges
- Bing's AI Topics Portfolio: How to Read Opportunity Queries
- TypeScript 7.1 Beta: The API That Lets You Leave TypeScript 6
- GitHub Apps Can Now Create Repos Without Admin Rights
- GitHub Actions Lockfiles: What actions.lock Pins and What It Doesn't
- pg_vectorsearch vs pgvector HNSW: Read the Benchmark Right
- uv 0.13 Breaking Changes: What Will Fail in Your CI
- pnpm 12.11 Can Install Agent Skills From Your Dependencies
- Google Now Wants Your AI-Written Metadata Fact-Checked Too
- Most Package Managers Don't Verify What They Download
- Google's UGC Fresh Data Program: Who Qualifies and Who Shouldn't
- Meta's New Crawl Terms: What robots.txt Still Controls
- pnpm Now Speaks Turborepo's Remote Cache API
- Copilot Code Review Bills the Pull Request Author
- Your SBOM Depends On Which Tool Generated It
- Deno Joins Cloudflare: One Year of Releases
- Python 3.15 Lazy Imports: Which Mode Pays
- Version Comparison Has No Standard
- A local model in Copilot CLI is not local privacy
- node:sqlite renamed DatabaseSync to Database
- pnpm 12.10 can install without a node_modules tree
- Copilot Local Sandboxing Is GA and Off by Default
- Copilot Usage Metrics Undercounted Your Agents
- The npm Read Path Has No Owner
- npm Will Never Publish Your .npmrc. It Will Publish Your .env.
- Git 3.0 Defaults to SHA-256. Nothing Can Talk To It.
- Python Wants a std Namespace Because PyPI Owns the Names
- GitHub's Async Merge API: Your Merge Bot Is Now Legacy
- npm Trusted Publishing Configs Now Expire in 48 Hours
- Rust Stops Shipping a 32-bit Windows Toolchain in 1.100
- The MCP Registry verifies namespaces, not servers
- GitHub's scheduled code scans may never start at all
- GitHub App tokens went from 40 to 520 characters
- MCP deprecated Roots, Sampling and Logging
- PyPI froze the HTML simple index API
- GitHub Now Rate-Limits Vulnerability Reports
- macOS 14 Runners Retire and Intel Is Missing
- npm 12 Blocks Install Scripts by Default
- pnpm 12 Is Now What You Install By Default
- AI Overviews: The Four Controls Google Documents
September 2026
- RubyGems 4.1: The Resolver Swap Is the Story
- Git 2.56: Which New Commands Actually Help
- Copilot Decides for You on 22 October
- Only Google Reads Your Schema Correctly
- The GitHub Actions API Now Stops Counting At 2,500
- Forum Schema Only Counts If Your Users Wrote It
- npm Retired The Audit Endpoints Your Tooling Still Calls
- Search Console's Multimodal Split, Explained
- Baseline 2026 Is Not Safe to Ship
- 826 Schema Types, About 30 Google Features
- Web Bot Auth: Crawlers That Sign Their Requests
- Bun 1.4 Absorbed Your Dependencies. Read the Stability Labels
- Google Added creator to VideoObject. It Is Not a Ranking Lever
- Next.js 15 Stops Getting Patches on October 21
- Scaled Content Abuse: What Google Actually Enforces
- pnpm 12.4 Now Installs Your Python and Rust Deps
- Chrome Removes XSLT: Your Styled Feed Goes Blank
- Next.js 16 Deleted Implicit Caching. Now You Ask.
- Google Will License EU Search Data. Not to You.
- Node Goes Annual. October Is When It Bites.
- Review Stars on Software Listings: Upvotes Aren't Ratings
- Google's Favicon Format List Has No SVG. Check Your Starter Template.
- pull_request_target Is Off by Default on Public Repos From 2 November
- Google Search Profiles: Who Actually Qualifies
- npm Stage-Only Tokens and the 2027 Deadline
- ubuntu-latest Becomes Ubuntu 26: What Breaks
- The CRA's 24-Hour Clock Started on 11 September
- Google's Aggregator Units Are Not an SEO Play
- Install Cooldowns: Four Tools, Four Unit Systems
- Search Console's AI Report Won't Show You Queries
- Node 26 Runs TypeScript. The Escape Hatch Is Gone.
- MCP Deleted the Handshake. Your 2025 Server Is Legacy.
- npm Took Away Your Publish Token. Good.
- llms.txt Is Not a Ranking Signal. Here's What Is.
- Vite 8 Swapped Its Bundler. Here's What Breaks.
- Google Killed FAQ Rich Results. Schema Still Earns Its Keep.
July 2026
- The TechLogHub Directory: Every Category of Developer and SaaS Tool We Track (2026)
- 10 AI Tools Worth Knowing in 2026 (Grouped by What They Actually Do)
- Programmatic SEO Without Thin Pages: Build the Gate Before the Generator
- Two Axes, 255 Tags: Designing a Taxonomy That Survives Real Data
- How to Actually Compare Developer Tools Without Reading 40 Landing Pages
- Startup Directories Ranked by Domain Authority (2026): The Honest List
- Where to Launch Your Startup: 12 Platforms Ranked by What You'll Actually Get (2026)
- Why Solo SEO is Dead: How Collaborative Growth Wins the SERPs
June 2026
- Microsoft quietly extends free Windows 10 ESU support to October 2027
- Data breach exposes up to 14.2 million email logins at six ISPs
- FBI: Russian Hackers Now Target Signal Backup Recovery Keys
- Clean GitHub repo tricks AI coding agents into running malware
- Stealthy Mistic backdoor linked to ransomware access broker KongTuke
- Windows 11 KB5095093 update rolls out new Point-in-Time restore feature
- Healthtech Firm Xsolis Suffers Data Breach Affecting 1.4 Million People
- Scattered Spider Members Plead Guilty to Hacking Transport for London
- The Exploit Doesn't Exist. You Can Still Prove It Works Against You
- LastPass confirms data breach in Klue supply chain attack
- WhatsApp phishing attack uses fake business docs to hack PCs
- FortiBleed campaign used custom FortiGate sniffer to steal credentials
- A Glimpse into the "Search Your Target" Market for Stolen Credentials
- AryStinger botnet infected thousands of D-Link routers worldwide
- New Prinz Eugen ransomware prioritizes recent files for encryption
- Microsoft links Mastra AI supply chain attack to North Korean hackers
- Klue OAuth breach victim list grows as Icarus hackers claim attack
- Hackers Exploit Unauthenticated Information Disclosure in Gravity SMTP WordPress Plugin
- Every AI Agent Is an Identity. Most Organizations Don't Treat Them That Way
- Webinar: How Attackers Bypass MFA and How Defenders Can Respond
- Microsoft: June 2026 Windows updates break Recycle Bin prompts
- CISA: Splunk Enterprise flaw actively exploited, patch by Sunday
- NY man charged after harassing college student with AI-generated nudes
- CISA warns Fortinet users to secure devices after FortiBleed leak
- Gentlemen ransomware's GentleKiller: 8 BYOVD EDR killers targeting 48 security products
- Nintendo confirms data stolen in WebMD subsidiary cyberattack
- USB Worm Spreads Crypto-Stealing Malware via Windows Shortcut Files
- Klue OAuth Breach Linked to Icarus Salesforce Data Theft Attacks
- 5 reasons Microsoft 365 backup isn’t enough for business data protection
- Police Clean Nearly 15,000 SocGholish-Infected Sites Tied to Evil Corp
- FortiBleed leak exposes Fortinet VPN credentials for 73,000 devices
- Why Account Takeovers Are Rising and How to Stop Them
- India's Telegram Ban Reaches the UAE: How to Bypass the Block with MTProto Proxy
- Microsoft confirms Office apps launch issues after June updates
- CISA orders feds to patch max severity Joomla plugin flaw by Friday
- Malicious JetBrains Marketplace Plugins Steal AI API Keys from Developers
- New Rokarolla Android malware targets 217 banking, crypto apps
- iRhythm breach: social engineering hit third-party SaaS apps; 360,000+ patients notified
- Ex-school district employee jailed for hacks on former employer
- phpBB forum fixes auth bypass bug lurking for a decade
- Maine disables data breach notification portal after fake disclosures
- Ukrainian national pleads guilty to role in Conti ransomware operation
- Over 400 Arch Linux packages compromised to push rootkit, infostealer
- Early Warning Signs of Supply-Chain Attacks Live in the Dark Web
- Microsoft Fixes Windows Update Failures Linked to WUSA Installer
- Novo Nordisk Discloses Breach of Clinical Trials Data
- Maine breach portal abused to publish fake data breach disclosures
- Oracle mitigates PeopleSoft zero-day exploited in data theft attacks
- AudiA6 crypto laundering service taken down: €336M allegedly washed for ransomware gangs
- Why AI-driven threats are exposing the limits of MSP security stacks
- Microsoft patches Exchange Server zero-day exploited in attacks
- The 5 Best Practices for Secure Identity Verification
- China-Linked JDY Botnet Expands Targeting of U.S. Military Networks
- Oracle PeopleSoft servers hacked in ShinyHunters data theft attacks
- GitHub announces npm security changes to tackle supply-chain attacks
- The Miasma worm source code briefly leaked on GitHub
- Microsoft patches YellowKey, GreenPlasma, MiniPlasma zero-days
- Path traversal flaw in AI dev platform Langflow exploited in attacks
- Reducing security operations complexity with Wazuh Cloud
- Check Point links VPN zero-day attacks to Qilin ransomware gang
- Oxford University discloses data breach after careers platform hack
- Over 20,000 Instagram accounts stolen in Meta AI support hack
- Hands on with Intelligent Terminal, an AI-powered Windows Terminal
- Critical Everest Forms Pro flaw exploited to take over WordPress sites
- Suspicious Polyfill login prompts pop up on Toshiba, Muji websites
- Chinese APT deploys new malware to keep access to hacked networks
- California Man Sentenced to More Than 26 Years for Fentanyl and Meth Trafficking on Nemesis Market (Dark Web)
- Cisco warns of unpatched SD-WAN zero-day exploited in attacks (CVE-2026-20245)
- Credit card theft campaign abuses Stripe to host stolen payment info
- DentaQuest Data Breach Exposes 2.6 Million Accounts
- UN food agency discloses breach affecting 600,000 Gaza households
- Microsoft Blames Caching Issue for Unexpected Windows Driver Updates
- French and Spanish Authorities Dismantle Fake ID Marketplace Used by Migrant Smugglers
- Chinese Hackers Use New Atlas RAT Malware in European Cyberattacks
- New HTTP/2 Bomb DoS Attack Crashes Web Servers in Under a Minute
- CISA warns of active attacks exploiting Android, Linux bugs
- What 345 Days of Untested Exposure Looks Like at a Bank
- Acer working to patch max severity zero-days in Wave 7 routers
- Operation KRATOS 2: 29 arrests, 9 IPTV piracy groups dismantled across 13 countries
- Google Adds Android Protection Against AI Deepfake Scam Calls
- VS Code zero-day lets hackers steal GitHub tokens in one click
- Over 116,000 Minecraft Systems Infected in WeedHack Malware Campaign
- AI-built ransomware toolkit automates EDR evasion, AD discovery
- Microsoft Exchange Online outage causes email delays, failures
- CISA flags two-year-old Oracle flaw as actively exploited in attacks
- Google fixes one actively exploited Android zero-day, 124 flaws
- Hackers hijack thousands of sites for ClickFix and FakeUpdate attacks
- WordPress malware campaign hides payloads in Steam profiles
- Microsoft confirms outage affecting MFA, My Sign-Ins platform
- Microsoft fixes KB5089549 Windows security update install issues
May 2026
- WP Maps Pro bug exploited to create admin accounts on WordPress sites
- Best Open Source Projects on GitHub in 2026: The Ones Worth Watching
- Vibe Coding in 2026: How Indie Founders Are Shipping SaaS Without Writing Code
- Best Developer Tools in 2026: The Complete Guide for Builders
- PAN-OS GlobalProtect VPN authentication bypass flaw (CVE-2026-0257) now exploited in attacks
- New CIFSwitch Linux flaw gives root on multiple distributions
- Google Chrome Adds Session Cookie Theft Protection for All Users
- North Carolina Man Sentenced to More Than 10 Years for Selling Personal Data of 7 Million Elderly Americans to Jamaican Scammers
- US charges Google security engineer with Polymarket insider trading
- Hackers exploit FortiClient EMS flaw to push infostealer malware
- FBI warns of fake FIFA websites running World Cup fraud schemes
- BTMOB Android malware service generates custom phishing payloads
- GreyVibe hackers use ChatGPT, Gemini to power cyberattacks
- Anthropic confirms Claude Mythos-class models will roll out to the public
- Charter Communications data breach affects 4.9 million accounts
- Carnival Cruise confirms data breach affecting nearly 6 million people
- Canadian Man Sentenced to 33 Years for Sextortion Targeting 145 U.S. Children
- GPU mining malware spreads via SEO poisoning, AI chatbots
- Can you enforce strong Active Directory password rules without frustrating users?
- Glassworm botnet disrupted after resilient C2 infrastructure takedown
- FBI warns of in-person data theft attacks from extortion gang
- CISA gives feds 4 days to patch actively exploited cPanel plugin flaw
- Dutch police arrests suspect linked to Ajax football club hack
- Windows 11 KB5089573 update released with performance improvements
- KnowledgeDeliver flaw exploited as a zero-day to install web shells
- Charter confirms data breach after ShinyHunters extortion threat
- CISA Orders Federal Agencies to Patch Actively Exploited Drupal Vulnerability
- Anthropic’s restricted Claude Mythos model may be coming to Claude Code
- FBI warns of Kali365 phishing service targeting Microsoft 365 accounts
- Ghost CMS SQL injection flaw exploited in large-scale ClickFix campaign
- Laravel Lang packages hijacked to deploy credential-stealing malware
- Italy Disrupts CINEMAGOAL Piracy App That Stole Streaming Auth Codes
- Netherlands Seizes 800 Servers Linked to Hosting Firm Behind Cyberattacks and Disinformation
- Former US execs plead guilty to aiding tech support scammers
- Google Exposes Unfixed Chromium Flaw That Keeps JavaScript Running in the Background
- Apple blocked over $11 billion in App Store fraud in six years
- Discord Rolls Out End-to-End Encryption for Voice and Video Calls
- Microsoft testing adjustable taskbar, Start menu in Windows 11
- Leaked Shai-Hulud malware fuels new npm infostealer campaign
- Grafana Breach Caused by Missed Token Rotation After TanStack Attack
- Webinar: The hidden bottlenecks in network incident response
- Microsoft confirms patching issues in restricted Windows networks
- Tycoon2FA hijacks Microsoft 365 accounts via device-code phishing
- Microsoft rejects critical Azure vulnerability report, no CVE issued
- Russian hackers turn Kazuar backdoor into modular P2P botnet
- Critical Funnel Builder WordPress Plugin Bug Exploited to Steal Credit Card Data on WooCommerce Checkouts
- Avada Builder WordPress plugin flaws allow site credential theft
- Microsoft to automatically roll back faulty Windows drivers
- Microsoft warns of Exchange zero-day flaw exploited in attacks
- TeamPCP Hackers Advertise Mistral AI Code Repos for Sale
- Hackers Exploit Auth Bypass Flaw in Burst Statistics WordPress Plugin
- Cisco warns of new critical SD-WAN flaw exploited in zero-day attacks (CVE-2026-20182)
- OpenAI Confirms Security Breach in TanStack Supply Chain Attack
- Windows 11 and Microsoft Edge hacked at Pwn2Own Berlin 2026
- KongTuke hackers now use Microsoft Teams for corporate breaches
- West Pharmaceutical says hackers stole data, encrypted systems
- New critical Exim mailer flaw allows remote code execution
- Windows BitLocker zero-day gives access to protected drives, PoC released
- Microsoft fixes Windows Autopatch bug installing restricted drivers
- Microsoft says some users can't install Office on Windows 365 devices
- US govt seeks Instructure testimony on massive Canvas cyberattack
- UK fines water supplier $1.3M for exposing data of 664k customers
- Instructure reaches 'agreement' with ShinyHunters to stop data leak
- Instructure confirms hackers used Canvas flaw to deface portals
- Webinar this week: Prevention alone is not enough against modern attacks
- Ivanti warns of new EPMM flaw exploited in zero-day attacks
- The Browser Is Breaking Your DLP: How Data Slips Past Modern Controls
- Americans sentenced for running 'laptop farms' for North Korea
- Palo Alto Networks firewall zero-day exploited for nearly a month
- Fake Claude AI website delivers new 'Beagle' Windows malware
- DAEMON Tools Devs Confirm Breach, Release Malware-Free Version
- Why ransomware attacks succeed even when backups exist
- Palo Alto Networks Warns of Firewall RCE Zero-Day Exploited in Attacks
- New stealthy Quasar Linux malware targets software developers
- Instructure Breach: Hacker Claims Data Theft From 8,800 Schools and Universities
- DAEMON Tools trojanized in supply-chain attack to deploy backdoor
- Student hacked Taiwan high-speed rail to trigger emergency brakes
- Vimeo data breach exposes personal information of 119,000 people
- Google now offers up to $1.5 million for some Android exploits
- Leaked AWS keys let phishers send through Amazon SES and pass SPF, DKIM and DMARC
- Backdoored PyTorch Lightning package drops credential stealer
- Trellix discloses data breach after source code repository hack
- They don’t hack, they borrow: How fraudsters target credit unions
- Instructure Confirms Data Breach as ShinyHunters Claims Attack
- Microsoft Defender wrongly flags DigiCert certs as Trojan:Win32/Cerdigent.A!dha
- Telegram Mini Apps Abused for Crypto Scams and Android Malware Delivery
- Critical cPanel flaw mass-exploited in "Sorry" ransomware attacks
- ConsentFix v3 Attacks Target Azure with Automated OAuth Abuse
- Microsoft tests modern Windows Run, says it's faster than legacy dialog
- Edu tech firm Instructure discloses cyber incident, probes impact
- 15-year-old detained over French govt agency data breach
- BleepingComputer retracts Instructure data breach story
- Criminal IP and Securonix ThreatQ Collaborate to Enhance Threat Intelligence Operations
- Microsoft fixes Remote Desktop warnings displaying incorrectly
- Two Former Ransomware Negotiators Sentenced to Four Years in Prison Over BlackCat (ALPHV) Attacks
- New Bluekit phishing service includes an AI assistant, 40 templates
- Romanian leader of online swatting ring gets 4 years in prison
April 2026
- New Linux Copy Fail flaw gives hackers root on major distros
- Hackers Exploit Authentication Bypass Flaws in Qinglong Task Scheduler to Deploy Cryptominers
- Hackers arrested for hijacking and selling 610,000 Roblox accounts
- cPanel, WHM emergency update fixes critical auth bypass bug
- Austria and Albania shut Tirana call centres behind €50M crypto investment fraud
- Learning from the Vercel breach: Shadow AI & OAuth sprawl
- GitHub fixes RCE flaw that gave access to millions of private repos
- CISA orders feds to patch Windows flaw exploited as zero-day
- Microsoft Says Backend Change Broke Teams Free Chat and Calls
- Video service Vimeo confirms Anodot breach exposed user data
- US reportedly charges Scattered Spider hacker arrested in Finland
- Checkmarx confirms LAPSUS$ hackers leaked its stolen GitHub data
- Microsoft to Deprecate Legacy TLS in Exchange Online Starting July 2026
- Inside an OPSEC Playbook: How Threat Actors Evade Detection
- Microsoft: New Remote Desktop warnings may display incorrectly
- Microsoft asks iPhone users to reauthenticate after Outlook outage
- Robinhood Account Creation Flaw Abused to Send Phishing Emails
- GlassWorm malware attacks return via 73 OpenVSX "sleeper" extensions
- Canada arrests three for operating “SMS blaster” device in Toronto
- Alleged Silk Typhoon/HAFNIUM hacker Xu Zewei extradited from Italy to the U.S.
- PyPI package with 1.1M monthly downloads hacked to push infostealer
- Microsoft rolls out revamped Windows Insider Program
- UNC6692 Uses Microsoft Teams to Deploy Snow Malware
- ADT confirms data breach after ShinyHunters leak threat
- New ‘Pack2TheRoot’ flaw gives hackers root Linux access
- DORA and operational resilience: Credential management as a financial risk control
- Over 10,000 Zimbra servers vulnerable to ongoing XSS attacks
- Microsoft now lets admins uninstall Copilot on enterprise devices
- Trigona Ransomware Attacks Use Custom Exfiltration Tool to Steal Data
- New Checkmarx supply-chain breach affects KICS analysis tool
- Kyber ransomware gang toys with post-quantum encryption on Windows
- Inside Caller-as-a-Service Fraud: The Scam Economy Has a Hiring Process
- Microsoft Releases Emergency Patches for Critical ASP.NET Core Privilege Escalation Flaw
- Over 1,300 Microsoft SharePoint servers vulnerable to spoofing attacks
- French govt agency confirms breach as hacker offers to sell data
- KelpDAO Hit by $290 Million Heist Linked to Lazarus Hackers
- China's Apple App Store infiltrated by crypto-stealing wallet apps
- The Gentlemen ransomware now uses SystemBC for bot-powered attacks
- NIST to stop rating non-priority flaws due to volume increase
- Vercel confirms breach as hackers claim to be selling stolen data
- Microsoft releases emergency updates to fix Windows Server issues
- Microsoft tests Windows Explorer speed, performance improvements
- Microsoft Pulls Service Update Causing Teams Launch Failures
- Seiko USA website defaced as hacker claims customer data theft
- Recently leaked Windows zero-days now exploited in attacks
- CISA flags Apache ActiveMQ flaw as actively exploited in attacks
- Webinar: From phishing to fallout — Why MSPs must rethink both security and recovery
- Inside an Underground Guide: How Threat Actors Vet Stolen Credit Card Shops
- Grinex Exchange Blames Western Intelligence for $13.7M Crypto Hack
- NAKIVO v11.2: Ransomware Defense, Faster Replication, vSphere 9, and Proxmox VE 9.0 Support
- Microsoft Teams right-click paste broken by Edge update bug
- AgingFly Malware Used in Attacks on Ukraine's Government and Hospitals
- Critical Nginx UI Authentication Bypass Flaw Now Actively Exploited in the Wild
- US nationals behind DPRK IT worker 'laptop farm' sent to prison
- Cisco says critical Webex Services flaw requires customer action
- Hackers exploit Marimo flaw to deploy NKAbuse malware from Hugging Face
- New Microsoft Defender "RedSun" zero-day PoC grants SYSTEM privileges
- Signed Dragon Boss adware disables antivirus on 23,500 hosts via abandoned updater
- Microsoft pays $2.3M to researchers at Zero Day Quest cloud and AI hacking event
- Microsoft: April updates trigger BitLocker key prompts on some servers
- Microsoft fixes bug behind Windows Server 2025 automatic upgrades
- Windows April 2026 updates add warnings for malicious .rdp files
- Kraken says criminals are extorting it after a support insider accessed client data
- 108 Chrome Web Store extensions share one C2 to harvest identities and sessions
- Fake Ledger Live app in Apple's Mac App Store tied to $9.5M in crypto theft
- Microsoft adds fast-track reinstatement after suspending WireGuard, VeraCrypt dev accounts
- Five identity-first Zero Trust controls engineering teams can actually ship
- European Gym giant Basic-Fit data breach affects 1 million members
- ShinyHunters leaks Rockstar analytics data taken via Anodot's Snowflake tokens
- wolfSSL CVE-2026-5194: missing digest checks let forged certificates verify
- Adobe patches exploited Acrobat Reader zero-day CVE-2026-34621 (APSB26-43)
- Storm infostealer moves browser decryption server-side to hijack sessions
- Critical Marimo Pre‑Authentication RCE Flaw Now Under Active Exploitation
- Over 20,000 crypto fraud victims identified in international crackdown
- ChatGPT launches a $100 Pro plan to compete with Claude's subscription.
- Microsoft: Canadian employees targeted in payroll pirate attacks
- LucidRook: Lua-based malware hits Taiwanese NGOs and universities
- VENOM phishing kit targets executives' Microsoft 365 logins with AiTM and device codes
- ChipSoft ransomware attack: Dutch EHR vendor's patient portals offline, data stolen
- Chrome 146 ships Device Bound Session Credentials to stop cookie theft
- Smart Slider updates hijacked to push malicious WordPress and Joomla versions
- When attackers already have the keys, MFA is just another door to open
- Webinar: From noise to signal – What threat actors are targeting next
- Eurail Reports December Data Breach Affecting 300,000 Travelers
- Hackers exploiting Acrobat Reader zero‑day flaw since December
- Hackers Steal $3.6 Million From Crypto‑ATM Giant Bitcoin Depot
- Microsoft suspends dev accounts for high‑profile open source projects
- ActiveMQ CVE-2026-34197: 13-year-old Jolokia bug enables remote code execution
- Is a $30,000 AI GPU better at password cracking than an RTX 5090?
- Microsoft fixes Windows 11 23H2 Start menu search broken by a Bing update
- Ninja Forms File Uploads flaw CVE-2026-0740 exploited to plant PHP webshells
- FBI IC3 2025 report: record $20.9 billion in cybercrime losses, up 26%
- Snowflake customer data stolen via tokens taken in a SaaS integrator breach
- US agencies warn Iran-affiliated hackers are disrupting Rockwell PLCs
- Flowise CVE-2025-59528 (CVSS 10) RCE now exploited in the wild
- APT28 hijacked SOHO router DNS to intercept Microsoft 365 logins
- Automated pentesting's 'PoC cliff': what it misses and how to fill the gaps
- Microsoft removes SaRA command-line tool from Windows; Get Help CLI replaces it
- Infostealers and stolen session cookies: why basic breach monitoring falls short
- FortiClient EMS zero-day CVE-2026-35616 exploited; hotfix out for 7.4.5 and 7.4.6
- React2Shell exploited to steal secrets from 766 Next.js hosts in automated campaign
- Axios npm hijack: fake Teams 'update' let North Korean hackers publish malware
- Device code phishing jumps 37x in 2026 as EvilTokens and copycat kits spread
- LinkedIn probes for 6,000+ Chrome extensions: what BrowserGate found and how it works
- Hims & Hers support-ticket breach: Zendesk reached through a hijacked Okta SSO account
- Die Linke confirms Qilin ransomware attack: staff data at risk, member database safe
- Multi-extortion ransomware explained: why backups alone no longer save you
- Exchange Online access bug hits Outlook mobile and new Outlook for Mac for weeks
- Engineer who locked out 254 servers in extortion plot pleads guilty, gets 32 months
- CERT-EU: Trivy supply-chain attack led to European Commission AWS breach
- Fake 'leaked Claude Code' GitHub repos push Vidar stealer and GhostSocks proxy
- Drift loses about $285M after attackers hijack its Solana Security Council multisig
- GreyNoise: residential proxy IPs rotate too fast for IP reputation to catch
- CrystalX RAT: new malware-as-a-service mixes stealer, clipper and prankware
- EvilTokens: phishing-as-a-service that abuses Microsoft's OAuth device code flow
- NoVoice Android rootkit hid in 50+ Google Play apps with 2.3 million downloads
- Chrome CVE-2026-5281: WebGPU Dawn zero-day is 2026's fourth exploited Chrome bug
- Blackpoint 2026 report: ClickFix, SSL VPN logins and RMM tools drove most intrusions
March 2026
- Citrix NetScaler CVE-2026-3055 memory overread exploited on SAML IdP appliances
- F5 reclassifies BIG-IP APM flaw CVE-2025-53521 as RCE after webshell attacks
- Microsoft pulls Windows 11 KB5079391 over 0x80073712 errors, ships KB5086672 fix
- FortiClient EMS SQL injection CVE-2026-21643 exploited: patch past 7.4.5
- European Commission breach traced to Trivy supply-chain attack and a stolen AWS key
- FBI confirms Iran-linked Handala hackers leaked Director Kash Patel's personal emails
- Smart Slider 3 flaw CVE-2026-3098 lets subscribers read wp-config.php on WordPress sites
- Backdoored Telnyx PyPI releases 4.87.1 and 4.87.2 hid a credential stealer in WAV audio
- Fake VS Code security alerts flood GitHub Discussions to lure developers to malware
- Agentic GRC: a vendor argues the hard part is the mindset, not the technology
- European Commission confirms data taken from AWS-hosted Europa web platform
- ACE shuts down AnimePlay, an Indonesian anime piracy app with 5 million users
- Windows 11 KB5079391 preview lets users toggle Smart App Control without a reinstall
- Dutch police disclose phishing breach, say impact limited and citizen data not exposed
- UK sanctions Xinbi, a $24B Telegram crypto marketplace serving scam centres
- Russia arrests suspected LeakBase admin weeks after FBI-Europol takedown
- Armenian man extradited to the US over alleged role in RedLine infostealer operation
- GitHub adds AI security detections for Shell, Dockerfiles, Terraform and PHP
- PolyShell: Magento file-upload flaw hit 56% of vulnerable stores in days
- Phishers use Bubble no-code apps on bubble.io to steal Microsoft logins
- Torg Grabber infostealer hits 728 crypto wallets and 103 password managers
- Citrix NetScaler CVE-2026-3055: SAML IdP memory leak exploited after patch
- Stolen and resold AI accounts and API keys are a growing underground trade
- Kali Linux 2026.1: 8 new tools, kernel 6.18 and a BackTrack mode
- TP-Link patches Archer NX router auth bypass that allows firmware upload
- Russian TA551 botnet co-manager gets 2 years over BitPaymer ransomware access
- PTC warns of imminent attacks on critical Windchill and FlexPLM RCE flaw CVE-2026-4681
- LiteLLM 1.82.7 and 1.82.8 on PyPI backdoored in TeamPCP supply-chain attack
- Firefox 149 adds a free built-in VPN with a 50GB monthly limit
- Microsoft fixes classic Outlook bug that stopped Gmail and Yahoo accounts syncing
- Dutch Finance Ministry breach traced to zero-day in login software
- Mazda says attackers exploited a warehouse system, exposing 692 staff and partner records
- Tycoon2FA phishing-as-a-service back to full volume days after Europol takedown
- TeamPCP's Kubernetes payload wipes Iranian nodes and backdoors the rest
- Crunchyroll confirms vendor breach of support tickets after 6.8M-user data theft claim
- Trivy supply-chain attack spreads to Docker Hub images and Aqua's GitHub org
- Varonis launches Atlas, an AI security platform for agents, LLMs and their data
- How to Fine-Tune Open Models Locally With Unsloth Studio
- What Unsloth Offers for Local Model Training and Inference
- FBI and CISA tie Signal account-hijacking phishing to Russian intelligence
- Oracle issues out-of-band fix for CVE-2026-21992 in Identity Manager (CVSS 9.8)
- Operation Alice: police shut 373,000 dark web scam sites and seize 287 servers
- CISA set a March 22 deadline for Cisco FMC flaw Interlock exploited as a zero-day
- Stryker wiper attack: hardening admin tools against Iran-linked destructive intrusions
- Musician pleads guilty to $8M AI-generated music streaming royalty fraud
- FBI seizes Handala leak sites after Intune mass-wipe attack on Stryker
- APT28 linked to Zimbra XSS attacks on Ukraine; CISA adds CVE-2025-66376 to KEV
- Aura breach: vishing call exposed ~900,000 records in an acquired firm's marketing tool
- ScreenConnect 26.1 fixes CVE-2026-3564, a machine-key flaw enabling session hijack
- Apple ships first Background Security Improvement to fix WebKit flaw CVE-2026-20643
- GlassWorm hits 400+ GitHub repos, npm packages and VS Code/OpenVSX extensions
- EU sanctions Integrity Technology, i-Soon and Emennet Pasargad over cyberattacks
- Securing AI agents: five identity controls engineering teams can apply now
- Stryker attack used Microsoft Intune's remote wipe to erase devices, no malware needed
- Exchange Online outage (EX1253275) blocked mailbox access across Outlook clients
- Shadow AI: how to find unsanctioned AI tools and stop data leaking into them
- Microsoft pulls Samsung Galaxy Connect from the Store after C: drive lockouts
- OpenAI: ChatGPT ads stayed US-only in March 2026 despite privacy policy talk
- Microsoft ships out-of-band Windows 11 hotpatch KB5084597 for RRAS RCE flaws
- AppsFlyer Web SDK served crypto-stealing JavaScript after a domain registrar incident
- Classic Outlook bugs: group creation errors, Gmail/Yahoo sync failures, missing cursor
- Chrome 146 emergency updates fix exploited V8 and Skia zero-days (CVE-2026-3910, -3909)
- Google paid a record $17.1M in bug bounties in 2025, and started paying for AI flaws
- Apple backports Coruna exploit-kit fixes to old iPhones with iOS 15.8.7 and 16.7.15
- Elementor Ally plugin SQL injection (CVE-2026-2413) leaves 250k+ WordPress sites exposed
- CISA adds n8n expression-injection RCE (CVE-2025-68613) to its exploited list
- Meta adds scam warnings to WhatsApp, Facebook and Messenger as account-linking fraud grows
- BlackSanta EDR killer hits HR teams via résumé ISOs and vulnerable drivers
- BeatBanker Android malware poses as Starlink app to mine Monero and plant a RAT
- Windows 10 KB5078885 ESU update: March 2026 fixes and the Secure Launch shutdown bug
- CISA: Ivanti EPM auth bypass CVE-2026-1603 exploited, agencies given two weeks
- Windows 10 KB5075039 fixes WinRE that wouldn't start after KB5068164
- ClawJacked: websites could brute-force and hijack local OpenClaw agents
- QuickLens Chrome extension went malicious after a sale, pushing ClickFix and crypto theft
February 2026
- Public Google API keys silently gained Gemini access, Truffle Security finds
- 1Campaign cloaking service helps malicious Google ads slip past reviewers and scanners
- Microsoft extends Copilot DLP to labeled Office files on local and third-party storage
- Classic Outlook bug hides the mouse pointer; Microsoft points to WebView2 traces
See what launched this week
One email a week: new and trending developer tools, fresh comparisons, and what shipped. Unsubscribe in one click.