



farfa.tech
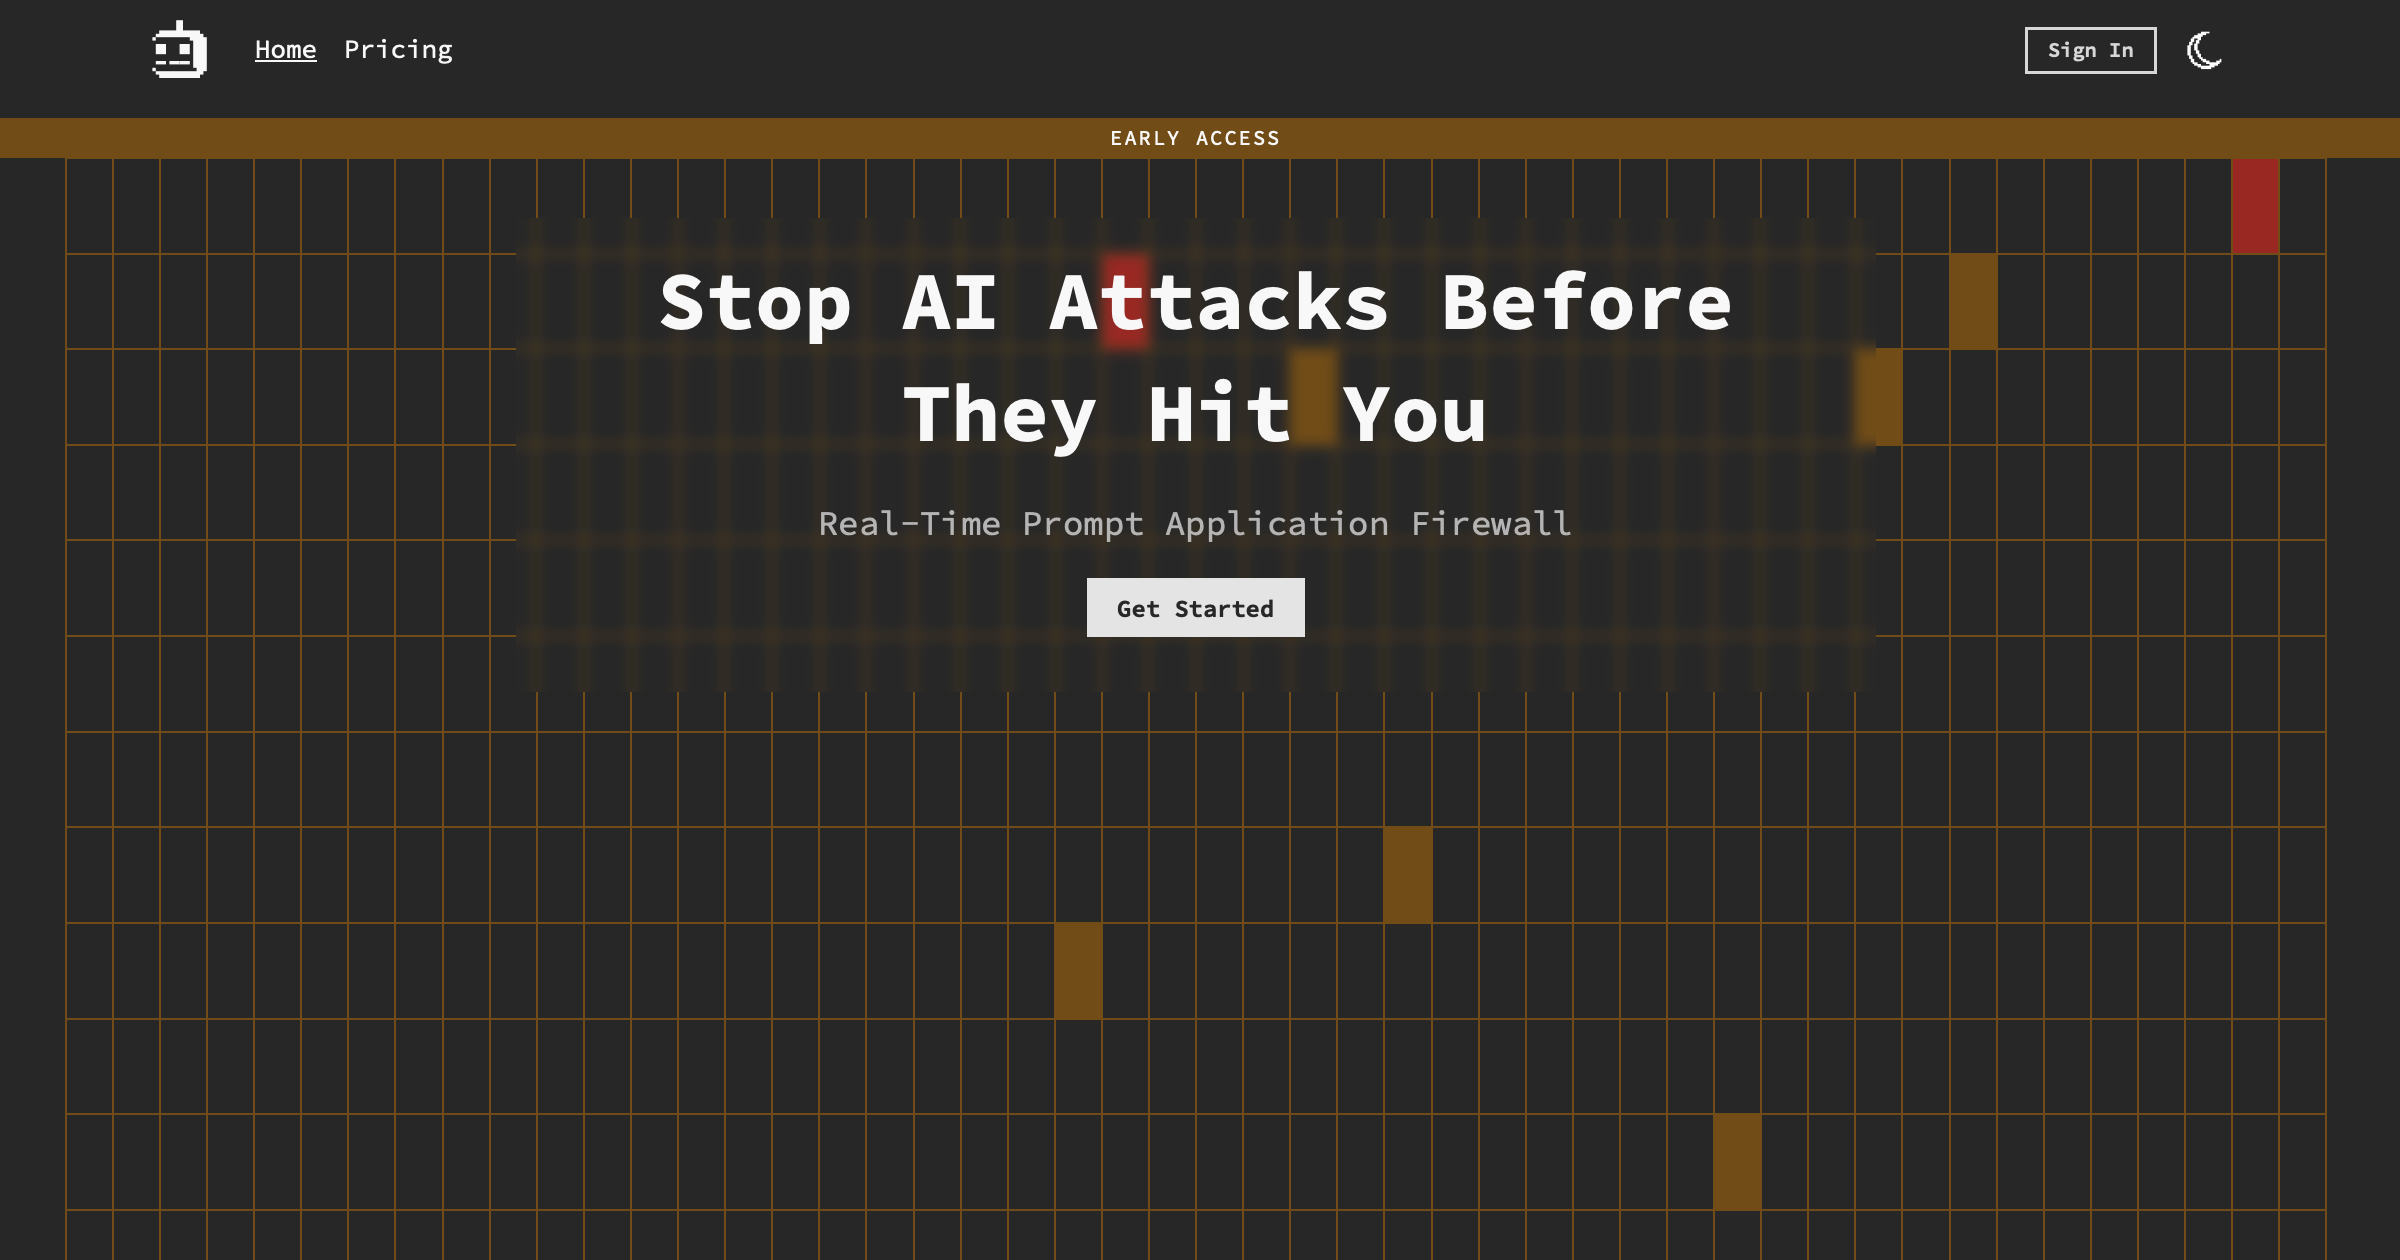
Real-Time Prompt Application Firewall (PAF) that detects and blocks prompt injection attacks on LLMs before they reach your systems.
About farfa.tech
Secure Your LLM Applications with Farfa's Real-Time Prompt Application Firewall
Farfa.tech provides a real-time prompt application firewall (PAF) that acts as a critical security layer between your users and your Large Language Models (LLMs). By intercepting and inspecting every prompt, Farfa ensures that only safe prompts reach your model, preventing malicious actors from hijacking your AI systems.
The platform is built for production-ready security with high performance and developer-friendly features.
How It Works: The Multi-Stage Pipeline
Every prompt passes through a rigorous multi-stage inspection pipeline. A request must survive all filters to reach your LLM, one red flag anywhere stops it cold.
- Vectorize: Embed the prompt into semantic space for deeper analysis.
- Static Analysis: Perform pattern and signature matching against known attack vectors.
- LLM Analysis: Utilize neural classifier scores to detect jailbreak intent.
- More Filters: Additional stages in the pipeline ensure comprehensive protection.
- Low Latency: Average request processing time is under 500ms across all stages.
- Safe Prompts Only: Only prompts that pass every filter are forwarded to your model.
Capabilities and Features
Farfa provides everything you need to secure your LLM from day one, designed for fast integration and transparent security.
- Real-Time Threat Blocking: Neutralize malicious prompts before they ever reach your model.
- Quick Integration: Route prompts through PAF in a few lines of code—minutes, not days.
- Low-Latency Filtering: Average request under 500ms, ensuring your users never feel the firewall.
- Staging Friendly: Validate integrations with a test API key (paf_sk_test_) for staging environments without production costs.
- Sandbox Playground: Try attack vectors against your configuration in the security-isolated sandbox playground.
- Team Collaboration & RBAC: Invite your team, engineers,s and developers to manage access at scale with Role-Based Access Control (RBAC).
- Usage-Based Pricing: Pay only for what you use with a flat fee plus usage costs, no hidden costs.
Why Security Matters Now
Prompt injection is not theoretical; it is a real vulnerability that has already been assigned critical CVEs in production tools like GitHub Copilot and Visual Studio.
- CVE-2025-53773: Command Injection in GitHub Copilot.
- CVE-2025-53773: Improper neutralization of special elements used in a command (command injection) in GitHub Copilot and Visual Studio allows an unauthorized attacker to execute code locally.
- Security Audit Exposure: 0% of AI systems assessed in security audits showed exposure to prompt injection vulnerabilities.
Integration Workflow
Integrating Farfa into your application is straightforward. Simply route prompts through the PAF API before forwarding them to your model.
- Send a POST request to the Farfa API with the user's prompt text.
- Include your unique API key in the headers.
- Receive a JSON response containing any detected matches.
- If the matches array is empty, the prompt is safe to forward to your LLM.
Value & Audience
Value Proposition
A real-time prompt application firewall that detects and blocks malicious injections before they reach your LLMs with sub-500ms latency.
Problem Solved
Prevents prompt injection attacks that can lead to data leaks, unauthorized code execution, and privilege escalation in LLM-powered applications.
Target Audience
Tech Stack
Backend
Social & Links
Social
Loading ratings...
Loading comments...
Gallery
Feedback & Roadmap
farfa.tech FAQ
Common questions about farfa.tech's features, pricing, and use cases
What does farfa.tech do?
A real-time prompt application firewall that detects and blocks malicious injections before they reach your LLMs with sub-500ms latency.
Is farfa.tech free to use?
farfa.tech is a paid product, starting at Staging Friendly: Validate integrations with a test API key - no production cost.. Full pricing tiers are listed on the farfa.tech product page on TechLogHub.
What problem does farfa.tech solve?
Prevents prompt injection attacks that can lead to data leaks, unauthorized code execution, and privilege escalation in LLM-powered applications.
Who is farfa.tech built for?
Developers and security teams building production AI applications using Large Language Models (LLMs).
What tech stack does farfa.tech use?
farfa.tech is built with TypeScript, Node.js, LLM Analysis, Neural Classifiers.
What category is farfa.tech listed under?
farfa.tech is listed in the Security & Privacy category on TechLogHub, alongside curated alternatives with community ratings and pricing comparisons.
farfa.tech appears in
You May Also Like
View all alternatives to farfa.techPresend
Free browser-based tools to clean, compress, and prepare files before you share them without ever uploading your data.
View Product
RoomGrade
AI-powered due diligence tool for founders to identify and mitigate red flags in their data rooms before investors conduct formal diligence.
View Product
Free Online Secret Message Encoder/Decoder
Encrypt and decrypt secret messages and files with AES-256 encryption in your browser.
View Product
SAM - Chrome Web Store
A powerful open-source adblocker featuring fingerprint protection and YouTube ad skipping.
View ProductOne email a week
TechLogHub tracks 510 tools and 471 open-source projects. Get the week's new launches, release roundups and open-source picks — nothing else.
Get the TechLogHub digest
One email a week: new and trending developer tools, fresh comparisons, and what shipped. Unsubscribe in one click.